Cyberattack shuts down refrigerators at French supermarkets
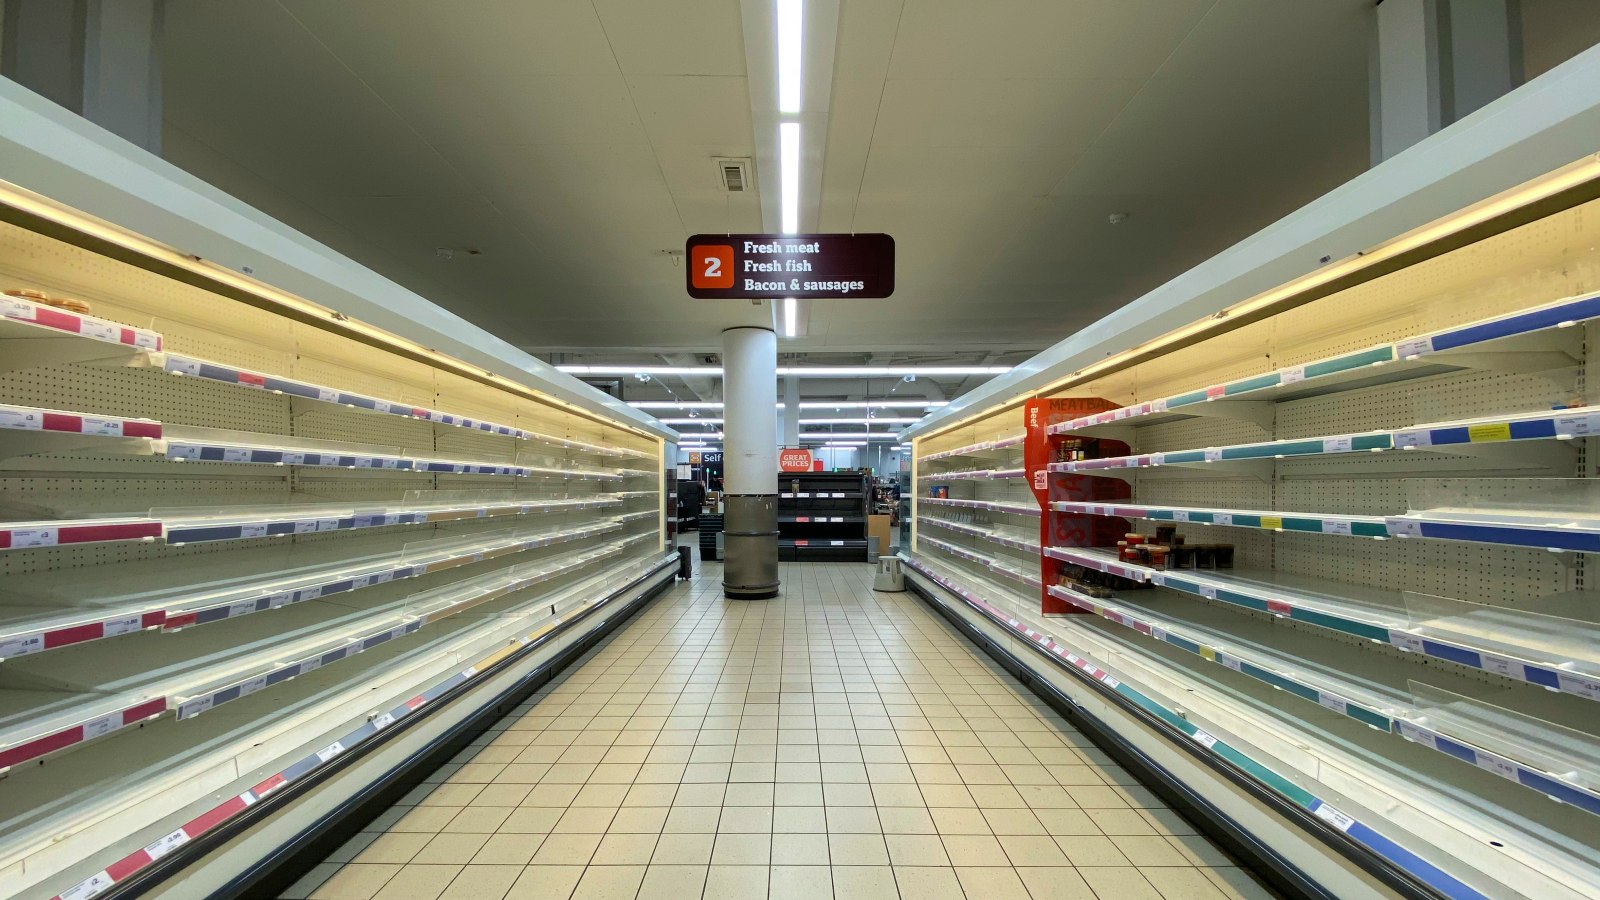
Attackers remotely defrosted refrigerators at multiple French supermarket chains overnight in a cyberattack that reportedly targeted Danfoss refrigeration controllers.
Victims include Intermarché, Coopérative U, Carrefour Market, Monoprix, Leclerc, and Super U, with French outlets reporting that the attack affected between 250 and 350 stores, causing significant financial losses and food waste.
The threat actors hijacked refrigeration controllers running older versions of Danfoss control software on Sunday night and used them to raise supermarket refrigerator temperatures by triggering a built-in automatic defrosting system.
Coopérative U president Dominique Schelcher confirmed the incident earlier today and said that the attack affected multiple stores in the chain.
"I can confirm that, since last night, a cyberattack has been affecting the refrigeration systems in several stores within our @CooperativeU network. Our teams are fully mobilized, working alongside refrigeration specialists, to resolve the situation as quickly as possible. An investigation will be conducted to shed full light on this attack," Schelcher said.
"Targeting equipment essential for preserving fresh produce and supplying food to the French people is an extremely serious matter and is unprecedented. It is unacceptable."
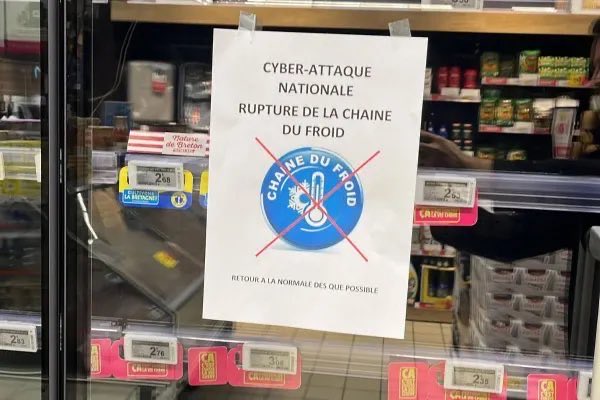 Cold chain breakage warning sign in French supermarket (Alejo Schapire)
EU agriculture and food commissioner Christophe Hansen also condemned the attack and named France's largest supermarket chain, Leclerc, as one of the victims.
The Paris prosecutor's office has told AFP that it has opened an investigation into "the large-scale cyberattack affecting the refrigerators of several major food retail chains across France" to "identify the victims and establish the link with the damage they reported in terms of foodstuff losses and the outbreak of fires."
While no information is available on how the attackers were able to compromise the Danfoss refrigeration controllers, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned in May 2025 of a high-severity authentication bypass vulnerability (CVE-2025-41450) in the Danfoss AK-SM 8xxA Series hardware platform used to manage refrigeration and HVAC systems typically found in the food retail sector.
Although there is no evidence yet that the two are connected, retail giant Ahold Delhaize, one of the world's largest food retail chains, also announced on Monday that it had to take some systems offline after a "cybersecurity incident."

Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0





Comments (0)